Decision 01
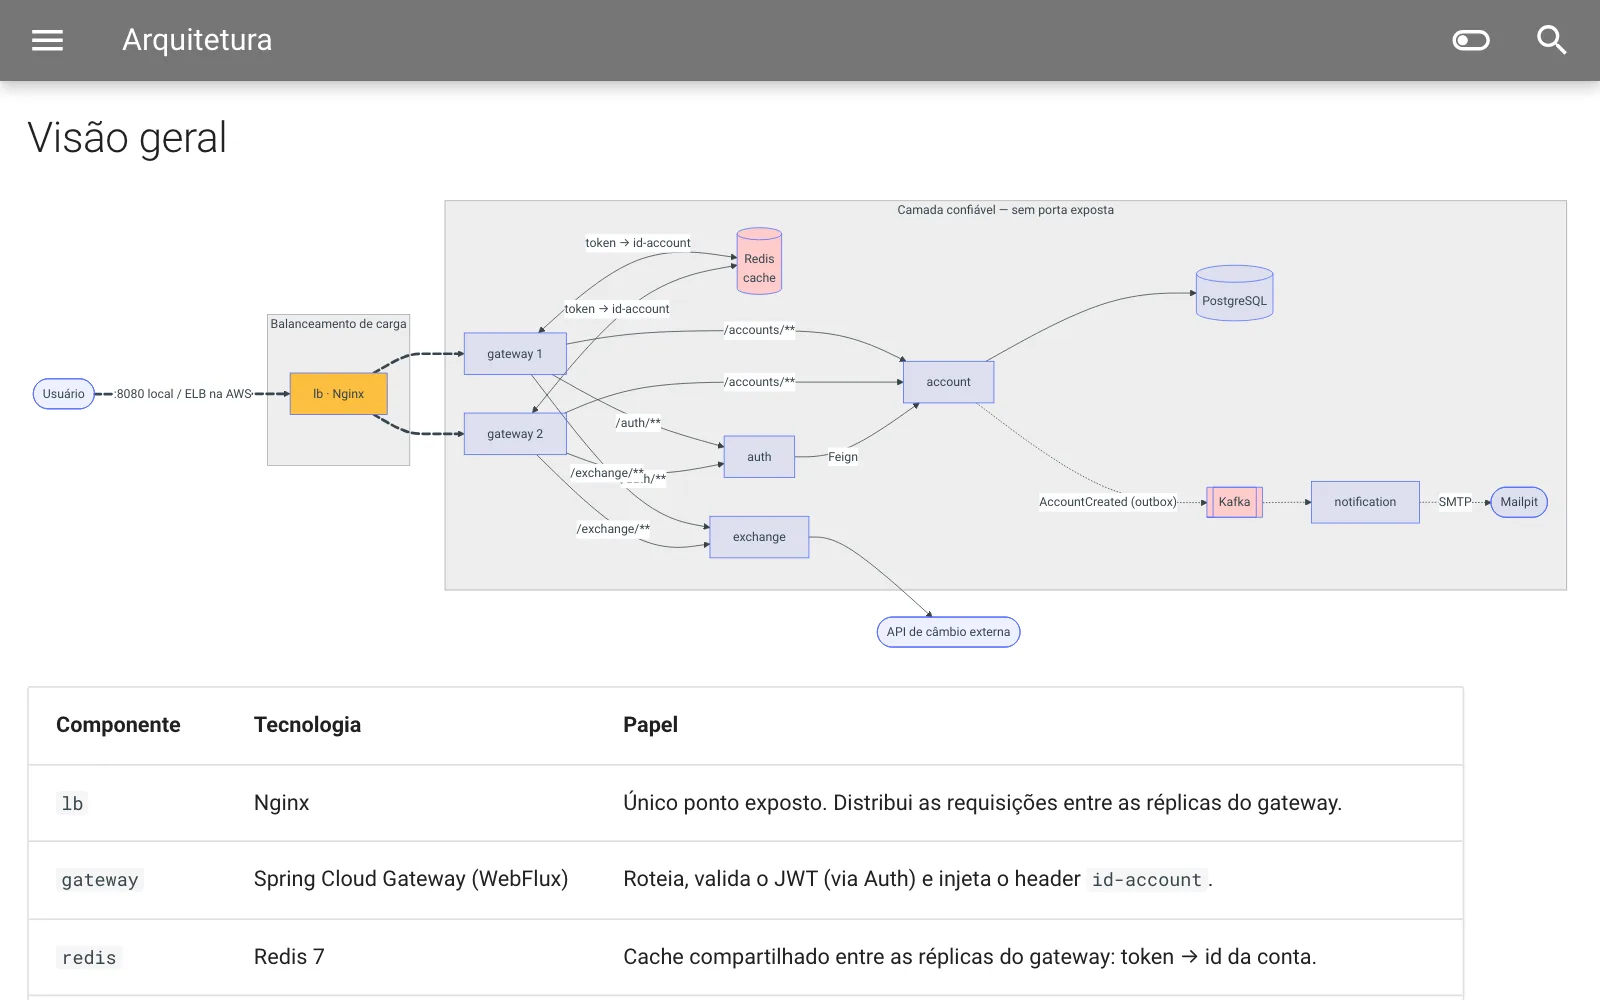
Question: Why store a hash of the token in Redis, and not the token?
Answer: The cache exists to take Auth out of every request's path, not to become a second place to steal a session from. With the key being the SHA-256 of the JWT, whoever reads Redis cannot reuse a single token; and since the TTL never goes past exp, an expired token does not stay valid because of the cache.